Managed Security Services (MSS)
Managed Security Services provide outsourced cybersecurity operations that protect organisations against evolving cyber threats. These services allow organisations to leverage expert security teams, advanced tools, and continuous monitoring without maintaining an in-house security operations centre.
1. Managed SOC Services:
Centralised security monitoring and incident response services that detect, investigate, and respond to cyber threats in real time.
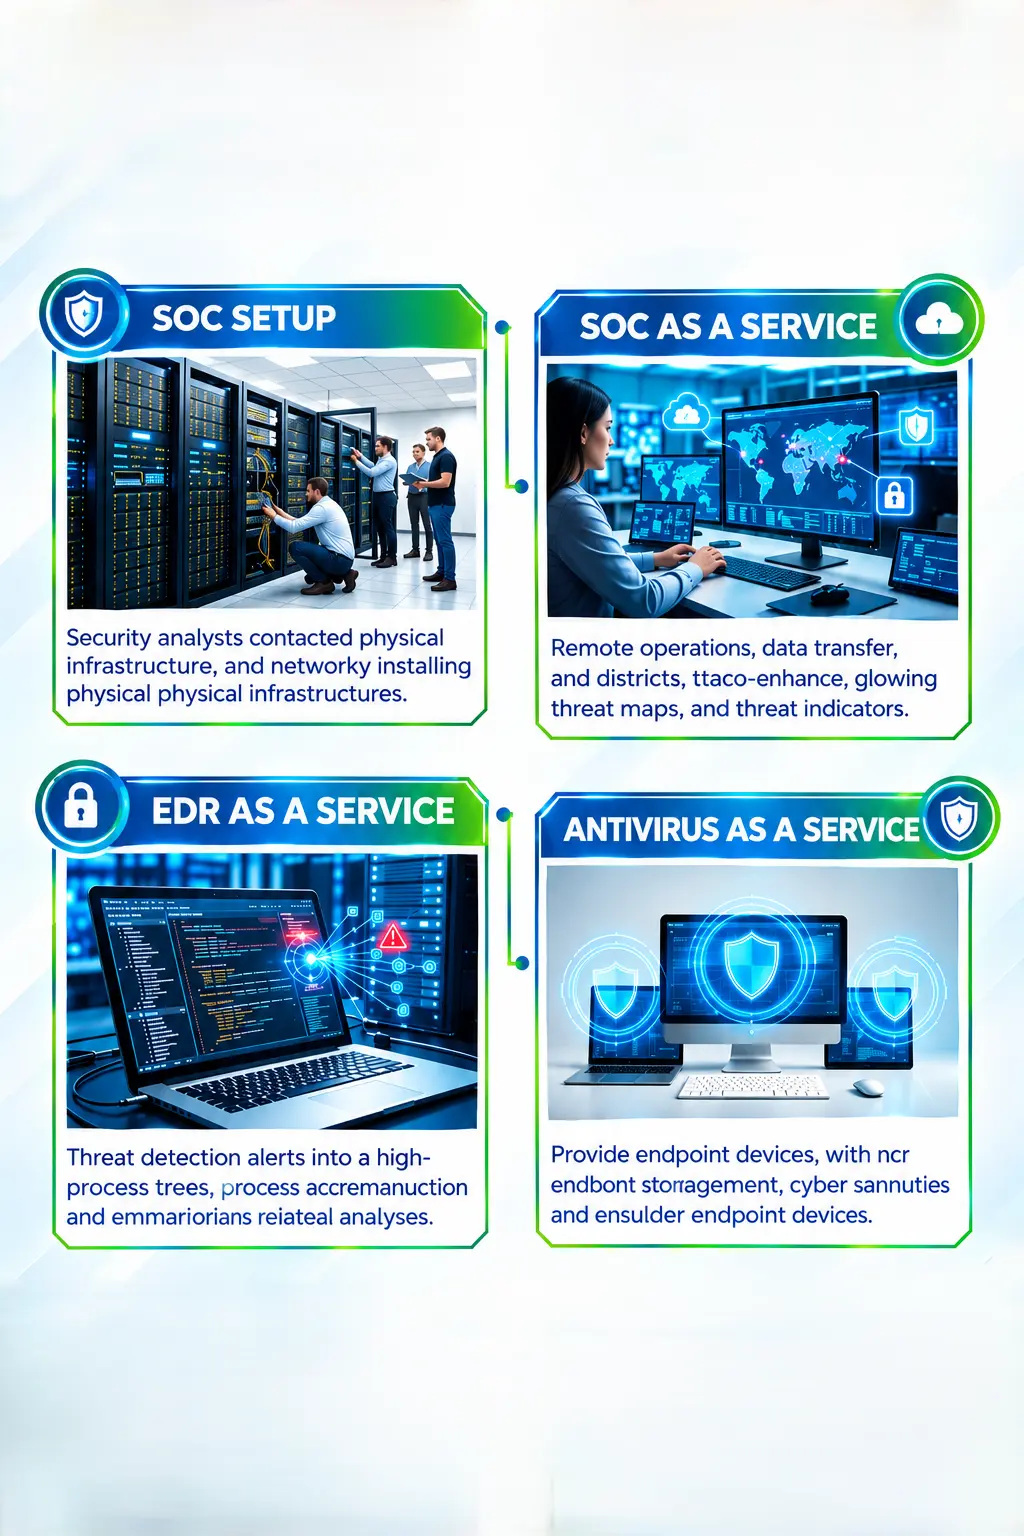
SOC Setup:
Designing and implementing a Security Operations Centre, including tools, processes, threat monitoring capabilities, and skilled analysts.
Setting up of SOC:
This setup empowers organisations with full visibility, proactive defence, and effective incident management.
SOC as a Service:
A fully managed SOC delivered from the cloud, providing 24/7 threat monitoring, detection, and incident response without the need for in-house infrastructure.
Service Includes:
EDR as a Service:
Managed endpoint detection and response that continuously monitors endpoints, detects suspicious behaviour, and automatically responds to threats.
Antivirus as a Service:
Cloud-managed endpoint protection that provides malware detection, automated updates, and centralised policy management across all devices.
2. Threat & Vulnerability Management:
Services focused on identifying, analysing, and mitigating security weaknesses before they can be exploited by attackers.
Vulnerability Assessment & Penetration Testing (VAPT):
Systematic identification of security vulnerabilities combined with simulated cyber-attacks to evaluate and strengthen system defences.
Security Assessment Services:
Comprehensive evaluation of security policies, processes, configurations, and controls to ensure compliance, resilience, and best practices.
3. Identity & Access Security:
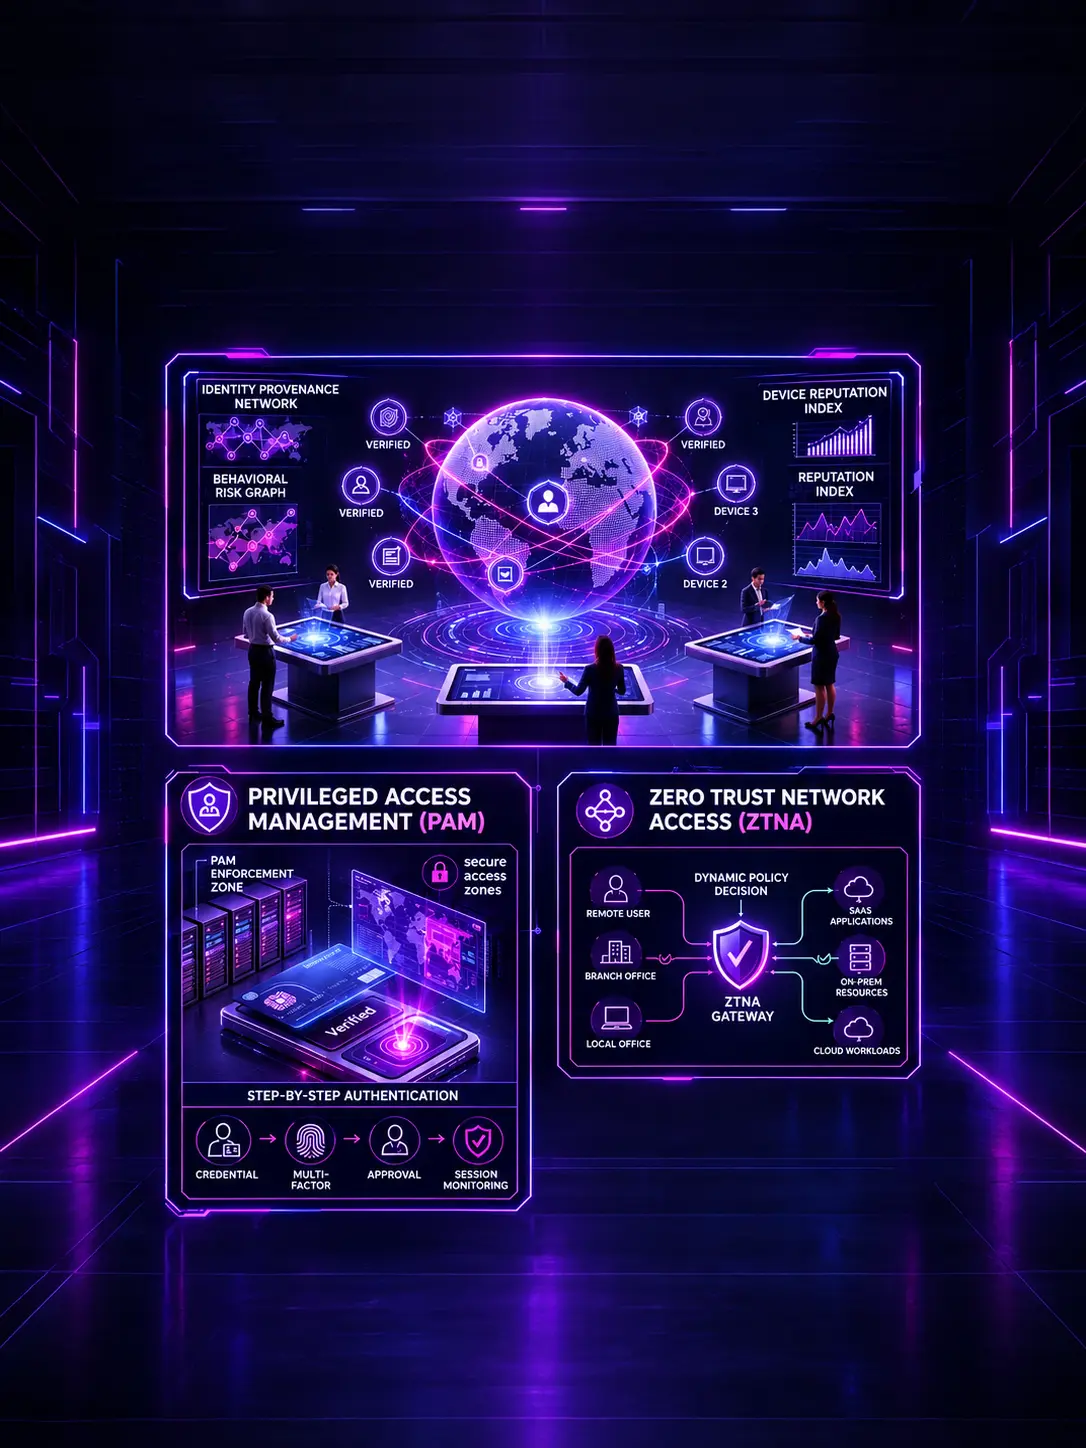
Security controls that ensure only authorised users can access systems, applications, and sensitive data.
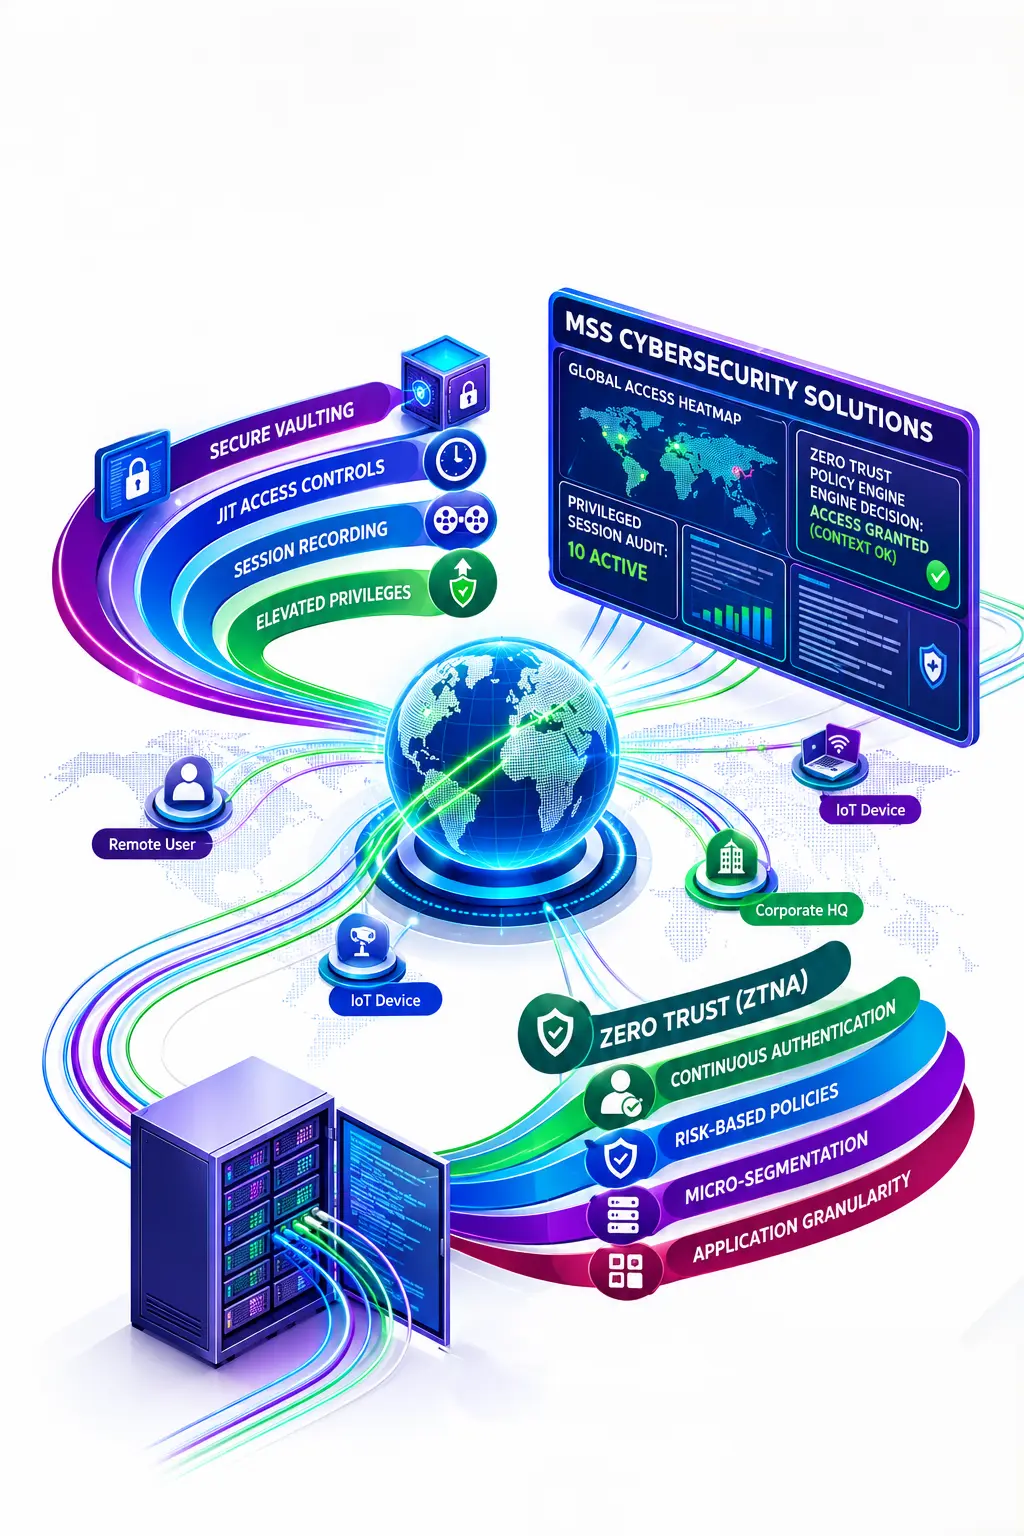
Privileged Access Management (PAM) as a Service:
Secure management of privileged accounts with controlled access, monitoring, and auditing to reduce insider threats and misuse.
Zero Trust Network Access (ZTNA) as a Service:
A security model that grants access based on strict identity verification and device posture, ensuring no user or device is trusted by default.
4. Data Security:
Technologies and processes designed to protect sensitive information from unauthorised access, leakage, or misuse.
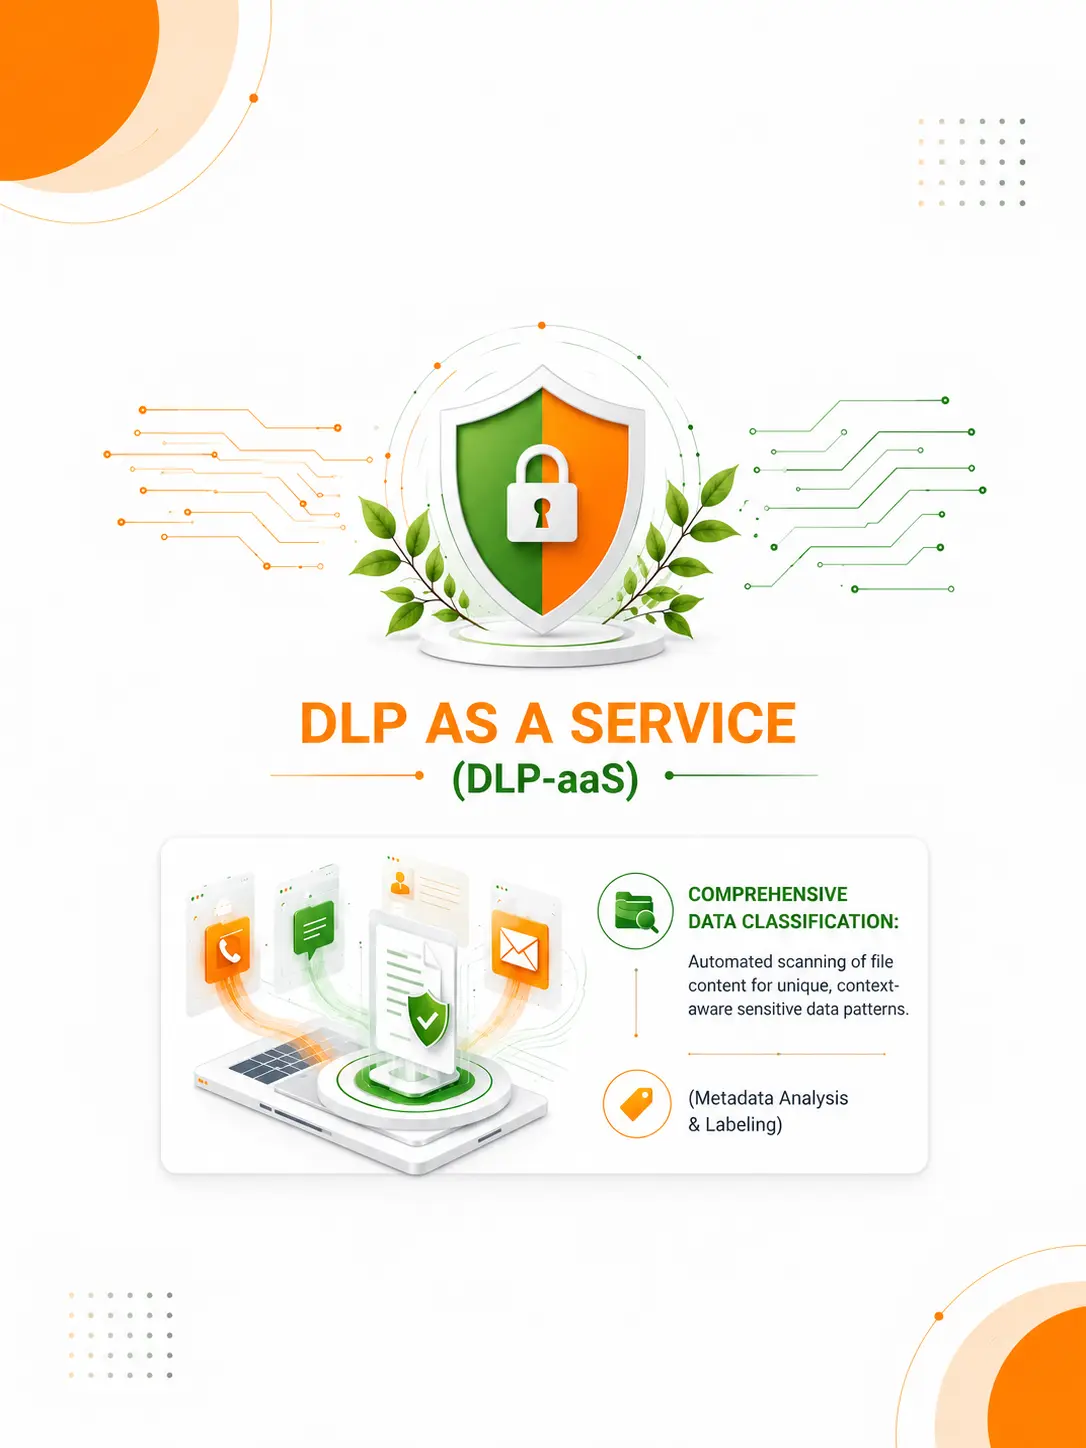
DLP as a Service:
Managed Data Loss Prevention that monitors and controls the movement of sensitive data to prevent leaks, breaches, or unauthorised sharing.
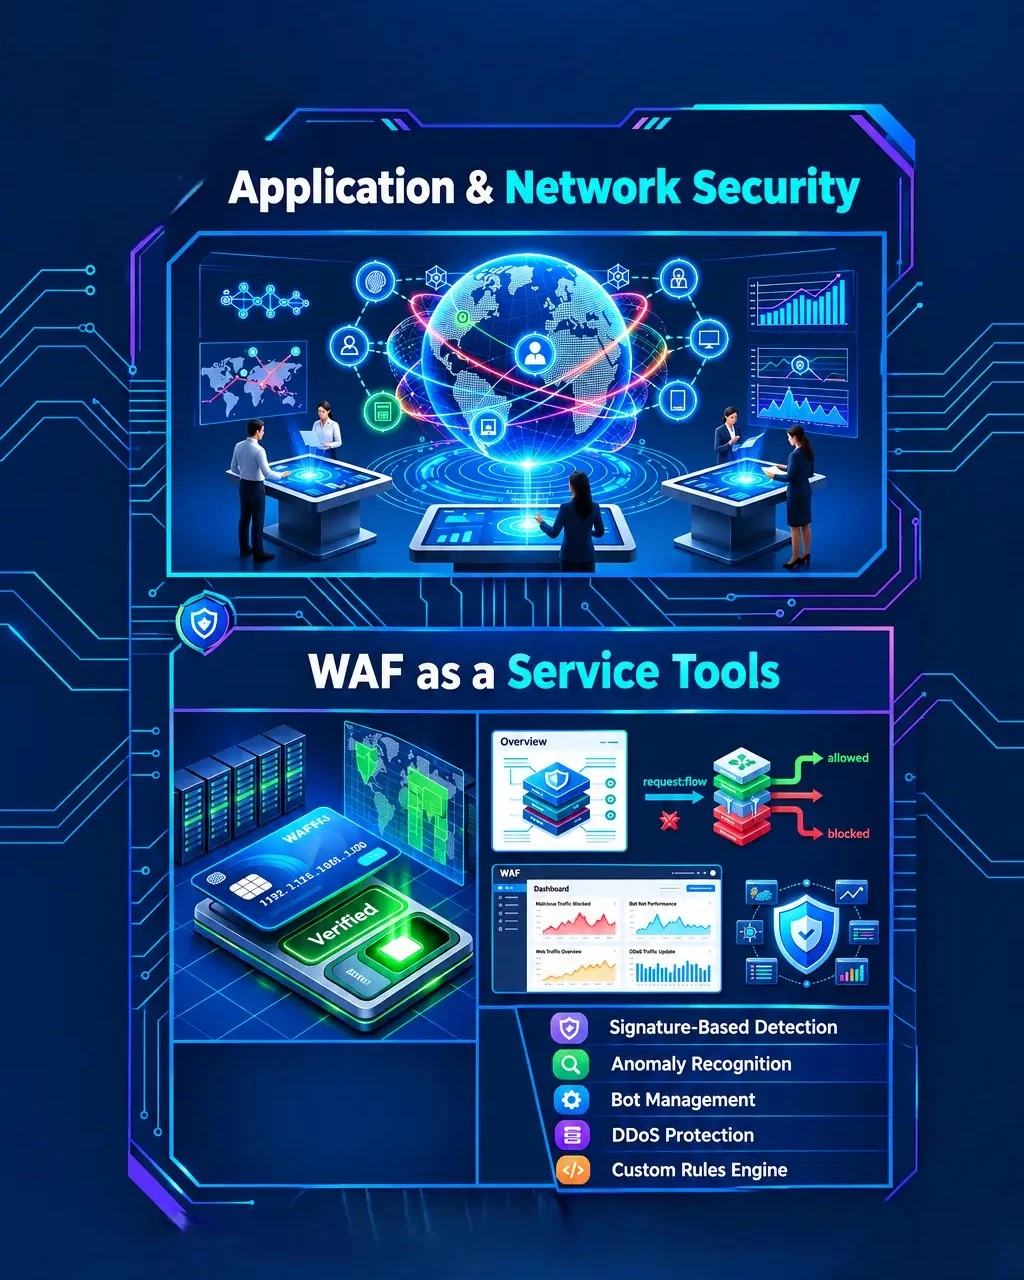
5. Application & Network Security:
Security services that protect applications and network infrastructure from cyberattacks and vulnerabilities.
WAF as a Service:
Cloud-based Web Application Firewall that protects web applications from attacks such as SQL injection, cross-site scripting (XSS), and other web threats.