Cybersecurity
Intelligent Cybersecurity Solutions
A proactive cybersecurity and a platform providing security information and event management (SIEM), threat detection, and log management. Featuring core components like the AI Engine, Data Processor, and Platform Manager. A strategy continues to support robust on-premises SIEM deployments Nodes: Single computers or servers joined in a cluster. Key security features:
Based on this foundation, we are providing focused, outcome-driven solutions designed around your business priorities.
Our Solutions
VAPT
Vulnerability Assessment and Penetration Testing identifies security weaknesses across applications, networks, systems, and infrastructure before attackers can exploit them. Regular assessments help organizations understand their current security exposure and prioritize remediation activities. Penetration testing validates whether identified weaknesses can be practically exploited. This proactive approach strengthens security posture and reduces the risk of successful cyberattacks.
Real Time Threat Detection and Response
Real-time threat detection continuously analyzes security events, network activity, endpoint behavior, and other indicators for suspicious activity. Advanced security technologies can identify potential threats and initiate response actions rapidly. Faster detection reduces the time attackers have to compromise systems or move across the environment. This capability helps organizations maintain stronger protection against evolving cyber threats.
Real Time Monitoring and Alerting
Continuous security monitoring provides centralized visibility into activities occurring across networks, endpoints, applications, and infrastructure. Security teams receive alerts when suspicious behavior, policy violations, or potential threats are detected. Real-time notifications enable faster investigation and response to security incidents. This improves situational awareness and helps organizations maintain continuous security operations.
Incident Investigation and Forensics
Incident investigation and digital forensics help security teams analyze suspicious events and determine how an attack occurred. Detailed examination of logs, system activity, network traffic, and other evidence helps identify root causes and affected assets. Findings can be used to strengthen security controls and prevent similar incidents. This process supports effective incident response, recovery, and continuous security improvement.
EDR and WAF
Endpoint Detection and Response solutions continuously monitor endpoint activities to identify suspicious behavior and potential compromise. Web Application Firewalls protect web applications from malicious requests and common application-layer attacks. Together, EDR and WAF technologies provide protection across both endpoint and application environments. Their combined capabilities strengthen an organization's layered cybersecurity strategy.
Compliance and Reporting
Security compliance and reporting capabilities help organizations monitor adherence to applicable security policies, regulations, and industry standards. Automated reporting provides structured visibility into security controls, incidents, vulnerabilities, and remediation activities. Consistent documentation simplifies audits and supports governance requirements. These capabilities also help organizations demonstrate security maturity to customers, partners, and regulatory stakeholders.
SIEM/SOAR – Security Orchestration Automation and Response
SIEM solutions collect, correlate, and analyze security events from across an organization’s IT environment to detect suspicious activities and potential threats. They provide centralized monitoring, real-time alerting, and security visibility to support faster threat detection and incident response.SOAR platforms integrate security tools and automate repetitive incident response workflows across the security environment. Automated playbooks can accelerate investigation, containment, and remediation activities. This reduces manual effort and enables security teams to respond consistently to recurring threats. SOAR improves operational efficiency while helping security teams handle a larger volume of security events.
Setting up SOC – Security Operation Center
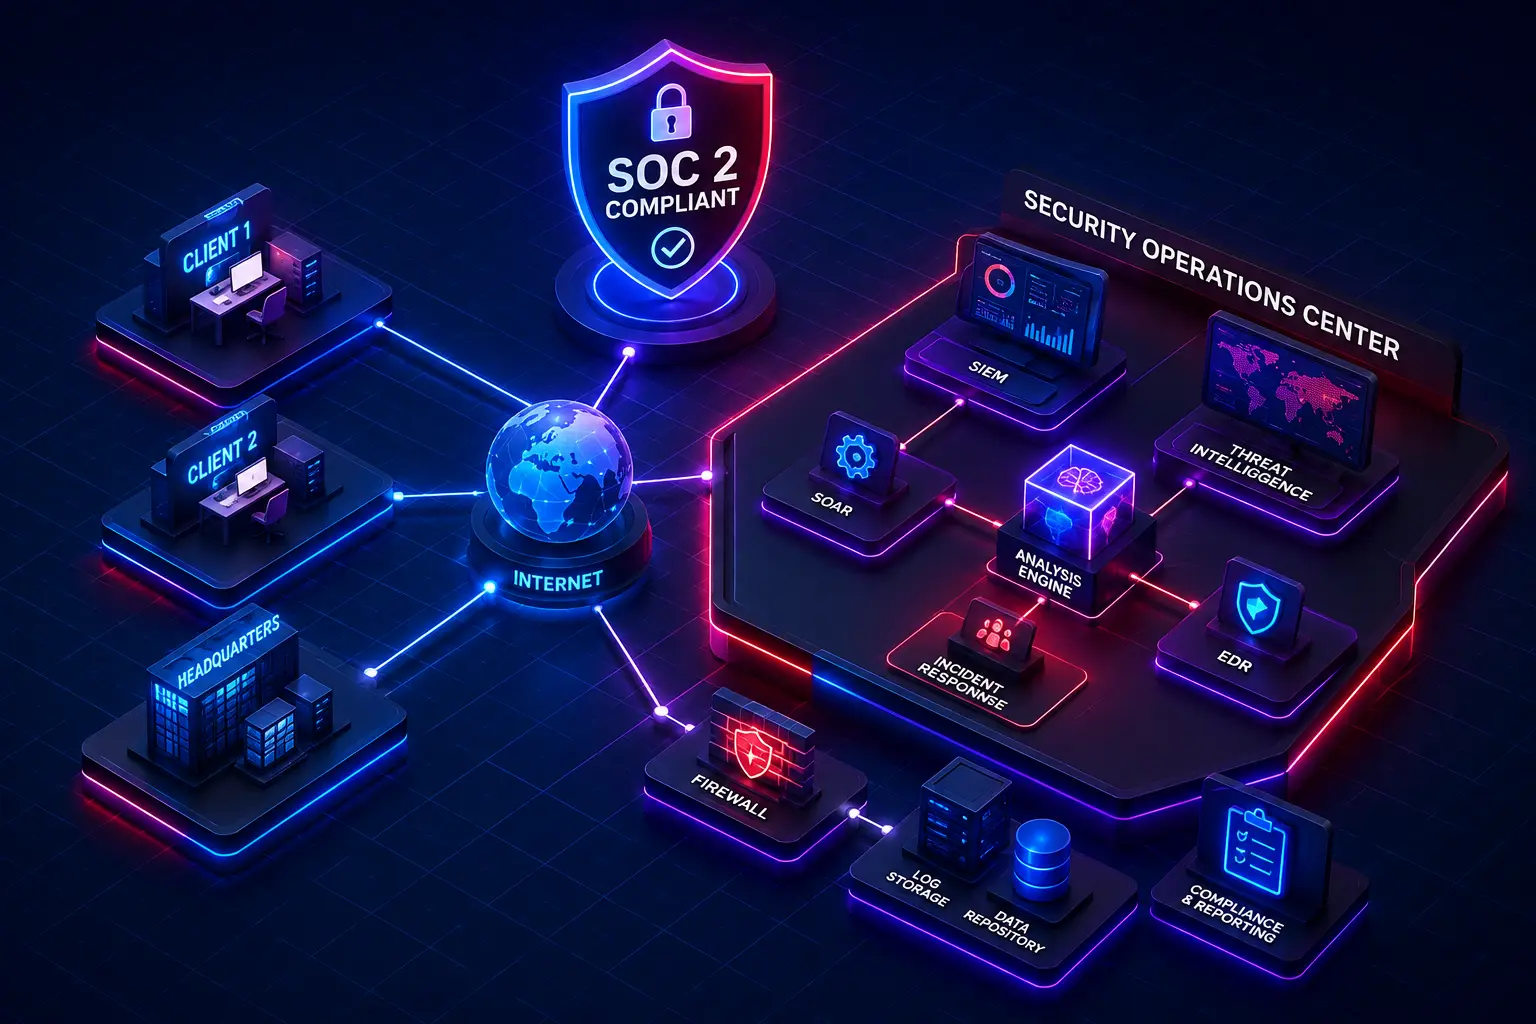
A Security Operations Center centralizes cybersecurity monitoring, threat detection, investigation, and incident response activities. SOC teams use security technologies such as SIEM, EDR, threat intelligence, and SOAR to maintain continuous visibility. Centralized operations enable faster identification and coordinated response to security incidents. A well-designed SOC provides an organized foundation for proactive and real-time enterprise security management.